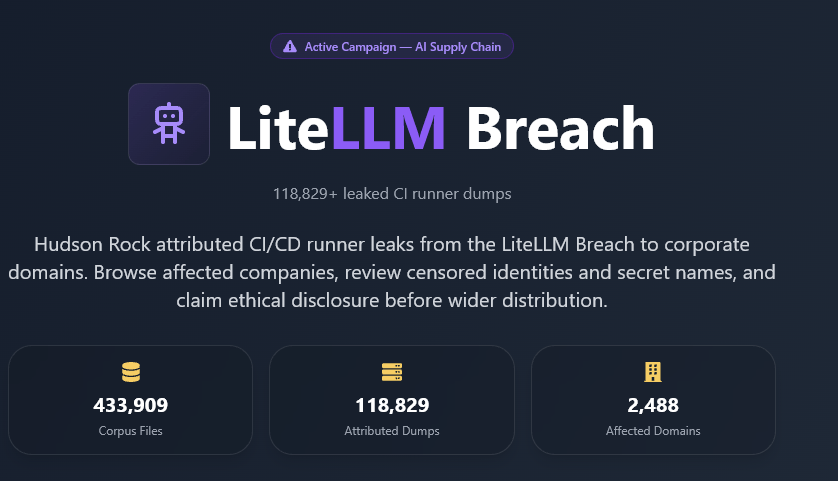
What if I told you that the very tools meant to protect your digital infrastructure were quietly weaponized against you? That’s exactly what happened in 2026, when a shadowy group called TeamPCP turned open-source security software into a backdoor for one of the most brazen supply chain attacks in history. The target? LiteLLM, an AI proxy gateway trusted by thousands of enterprises. The fallout? A 153GB data dump containing secrets from Amazon, Samsung, Cisco, and even Epic Games. This isn’t just a breach—it’s a wake-up call about the fragility of our digital ecosystems.
Let’s unpack this. TeamPCP didn’t start with LiteLLM. They began by poisoning Trivy, a popular open-source vulnerability scanner. How? By compromising its GitHub Actions pipeline. This allowed them to steal LiteLLM’s PyPI publishing tokens, which they used to inject malicious code into versions 1.82.7 and 1.82.8 of the package. What makes this particularly fascinating is the sophistication of the payload. The malware used a .pth Python hook to execute automatically when the Python interpreter initialized—meaning it didn’t even need to be explicitly imported. This is like a Trojan horse that activates the moment you turn on your computer, regardless of what you’re doing. It’s not just stealthy; it’s insidious.
Now, here’s where it gets even more alarming: the 153GB database of stolen data. Hudson Rock, the cybersecurity firm that uncovered this, found 433,909 files, including 118,829 CI runner dumps linked to 2,488 corporate domains. But here’s the kicker—many of these files lack clear attribution. Think about that. Your company’s secrets could be sitting in a database, unclaimed, while you’re blissfully unaware. Why? Because CI/CD pipelines are often configured generically. You might have a database password or an API key in there without any trace of your company’s domain or email. This is the ‘unattributed secrets problem’—a ticking time bomb waiting to be exploited.
Take the case of AdsWizz, a subsidiary of SiriusXM. The breach was traced through infrastructure markers like gitlab.adswizz.com, not just the committer’s email. This highlights a critical flaw in how we track cyberattacks: we rely too much on surface-level data. If you’re a SOC team, you need to dig deeper. Look at the endpoints, the server names, the network traffic. Don’t trust the email in the pipeline run. That’s how attackers game the system. And let’s be honest, how many of us have ever checked the infrastructure boundaries of our CI/CD pipelines? Probably not enough.
The list of impacted organizations reads like a who’s who of global tech: AWS, Samsung, Cisco, Salesforce, and even John Deere. This isn’t just a niche issue—it’s a systemic failure. The fact that LiteLLM was an open-source tool makes this even more dangerous. Open-source software is the backbone of modern development, but it’s also a honeypot for attackers. When a single vulnerability in a widely used tool can compromise thousands of enterprises, we’re not just talking about a security flaw. We’re talking about a crisis of trust in the open-source ecosystem.
And yet, here’s the thing: this attack could have been prevented. The solution isn’t just about revoking credentials or patching code. It’s about rethinking how we approach security in the age of AI and continuous integration. We need to stop treating security as an afterthought. Every line of code, every CI/CD pipeline, every third-party scanner should be treated as a potential entry point. That means auditing not just the tools we use, but the people who maintain them. Because if a vulnerability scanner can be compromised, what’s stopping someone from compromising a machine learning model or a cloud provider’s API?
The ethical disclosure process is a start, but it’s not enough. Organizations need to demand transparency from their vendors and open-source maintainers. They need to invest in threat intelligence platforms that can detect anomalies in real time. And they need to educate their developers about the risks of using third-party tools without scrutiny. Because in the end, the real enemy isn’t just TeamPCP. It’s the complacency that allows such attacks to go unnoticed until it’s too late.
So, what does this mean for the future? I think we’re seeing the beginning of a new era in cybersecurity—one where the lines between open-source tools, AI infrastructure, and corporate secrets blur. The LiteLLM breach isn’t an isolated incident; it’s a harbinger of things to come. If you’re not already auditing your CI/CD pipelines for suspicious activity, now is the time to start. Because in a world where the tools that protect you can also betray you, vigilance isn’t just a virtue. It’s a necessity.